


Check Real Cisco 300-710 Exam Question for Free (2026)
Get Ready to Boost your Prepare for your 300-710 Exam with 423 Questions
Cisco 300-710 certification exam is a highly sought after certification that is designed to validate the skills and knowledge of IT professionals in securing networks with Cisco Firepower. Securing Networks with Cisco Firepower certification exam is ideal for individuals who are interested in advancing their careers in network security and gaining recognition for their expertise in this field. With this certification, IT professionals can demonstrate their ability to secure network infrastructure, identify and mitigate security threats, and ensure compliance with industry standards.
NEW QUESTION # 102
How should a high-availability pair of Cisco Secure Firewall Threat Defense Virtual appliances be deployed to Cisco Secure Firewall Management Center?
- A. Configure high availability first, then add the primary and secondary appliances to Cisco Secure Firewall Management Center.
- B. Configure high availability first, then add only the primary Cisco Secure Firewall Threat Defense Virtual appliance to Cisco Secure Firewall Management Center.
- C. Add the primary appliance to Cisco Secure Firewall Management Center first, then configure high availability.
- D. Add the primary and secondary Cisco Secure Firewall Threat Defense Virtual appliances to Cisco Secure Firewall Management Center first, then configure high availability.
Answer: A
NEW QUESTION # 103
With Cisco FTD integrated routing and bridging, which interface does the bridge group use to communicate with a routed interface?
- A. switch virtual
- B. subinterface
- C. bridge group member
- D. bridge virtual
Answer: D
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/640/configuration/guide/fpmc-config-guide-v64/transp
NEW QUESTION # 104
What is the role of the casebook feature in Cisco Threat Response?
- A. sharing threat analysts
- B. triage automaton with alerting
- C. pulling data via the browser extension
- D. alert prioritization
Answer: A
Explanation:
Explanation
The casebook and pivot menu are widgets available in Cisco Threat Response. Casebook - It is used to record, organize, and share sets of observables of interest primarily during an investigation and threat analysis. You can use a casebook to get the current verdicts or dispositions on the observables.
https://www.cisco.com/c/en/us/td/docs/se
curity/ces/user_guide/esa_user_guide_13-5-1/b_ESA_Admin_Guide_ces
_13-5-1/b_ESA_Admin_Guide_13-0_chapter_0110001.pdf
NEW QUESTION # 105
An engineer is configuring a second Cisco FMC as a standby device but is unable to register with the active unit. What is causing this issue?
- A. The primary FMC currently has devices connected to it.
- B. The code versions running on the Cisco FMC devices are different
- C. There is only 10 Mbps of bandwidth between the two devices.
- D. The licensing purchased does not include high availability
Answer: B
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config-guide-v62/firepo
NEW QUESTION # 106
Refer to the exhibit. An administrator is looking at some of the reporting capabilities for Cisco Firepower and noticed this section of the Network Risk report showing a lot of SSL activity that cloud be used for evasion. Which action will mitigate this risk?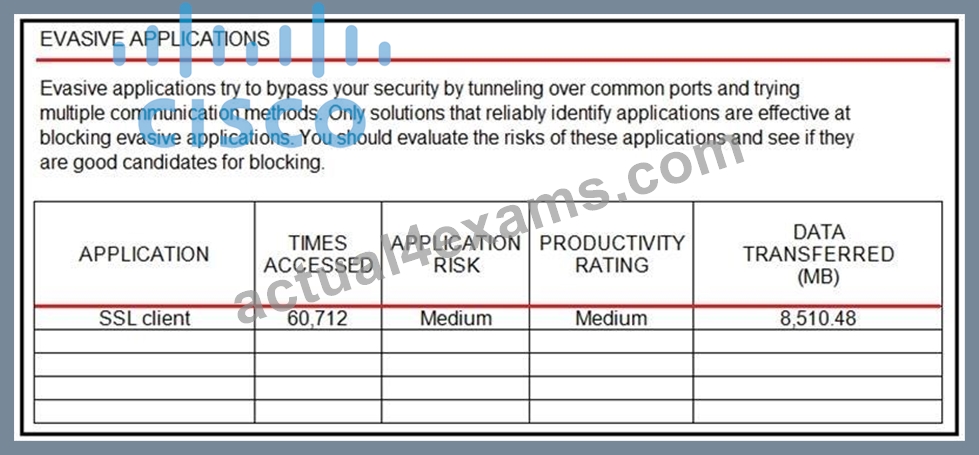
- A. Use encrypted traffic analytics to detect attacks
- B. Use Cisco AMP for Endpoints to block all SSL connection
- C. Use Cisco Tetration to track SSL connections to servers.
- D. Use SSL decryption to analyze the packets.
Answer: D
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/firepower/623/fdm/fptd-fdm-config-guide-623/fptd- fdm-ssl-decryption.html
NEW QUESTION # 107
Which Cisco Advanced Malware Protection for Endpoints policy is used only for monitoring endpoint actively?
- A. audit
- B. Windows domain controller
- C. protection
- D. triage
Answer: A
NEW QUESTION # 108
A network engineer is configuring URL Filtering on Firepower Threat Defense. Which two port requirements on the Firepower Management Center must be validated to allow communication with the cloud service? (Choose two.)
- A. outbound port TCP/443
- B. outbound port TCP/8080
- C. inbound port TCP/443
- D. outbound port TCP/80
- E. inbound port TCP/80
Answer: A,D
Explanation:
https://www.cisco.com/c/en/us/support/docs/security/firesight-management-center/118852-technote-firesight-00.html
https://community.cisco.com/t5/security-documents/ftd-url-filtering-how-it-works/ta-p/3347292
NEW QUESTION # 109
Drag and drop the steps to restore an automatic device registration failure on the standby Cisco FMC from the left into the correct order on the right. Not all options are used.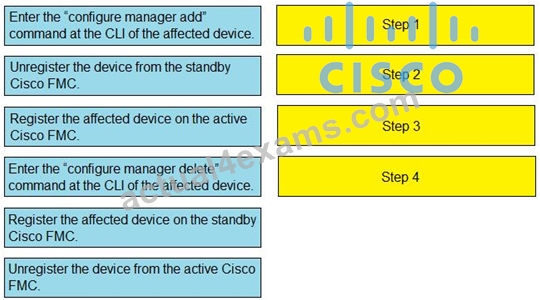
Answer:
Explanation: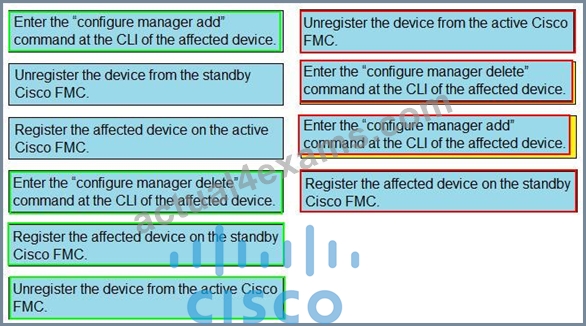
NEW QUESTION # 110
What is the result of specifying of QoS rule that has a rate limit that is greater than the maximum throughput of an interface?
- A. The system rate-limits all traffic.
- B. The system repeatedly generates warnings.
- C. Matching traffic is not rate limited.
- D. The rate-limiting rule is disabled.
Answer: C
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config- guide-v62/quality_of_service_qos.pdf
NEW QUESTION # 111
Refer to the exhibit.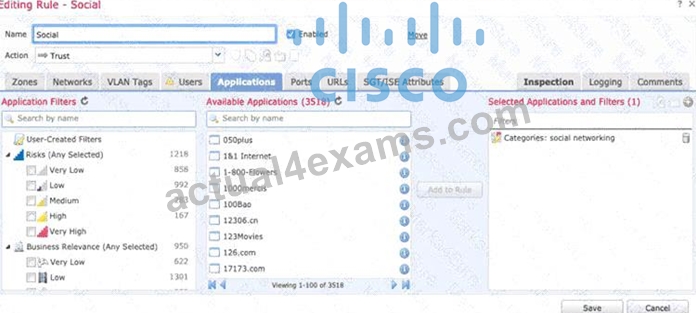
An organization has an access control rule with the intention of sending all social media traffic for inspection After using the rule for some time, the administrator notices that the traffic is not being inspected, but is being automatically allowed What must be done to address this issue?
- A. Modify the rule action from trust to allow
- B. Modify the selected application within the rule
- C. Add the social network URLs to the block list
- D. Change the intrusion policy to connectivity over security.
Answer: B
NEW QUESTION # 112
A company is in the process of deploying intrusion prevention with Cisco FTDs managed by a Cisco FMC. An engineer must configure policies to detect potential intrusions but not block the suspicious traffic. Which action accomplishes this task?
- A. Configure IDS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by checking the "Drop when inline" option.
- B. Configure IDS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by unchecking the "Drop when inline" option.
- C. Configure IPS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by unchecking the "Drop when inline" option.
- D. Configure IPS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by checking the "Drop when inline" option.
Answer: C
NEW QUESTION # 113
The CIO asks a network administrator to present to management a dashboard that shows custom analysis tables for the top DNS queries URL category statistics, and the URL reputation statistics.
Which action must the administrator take to quickly produce this information for management?
- A. Copy the intrusion events dashboard tab and modify each widget to show the correct charts.
- B. Create a new dashboard and add three custom analysis widgets that specify the tables needed.
- C. Run the Attack report and filter on DNS to show this information.
- D. Modify the Connection Events dashboard to display the information in a view for management.
Answer: B
NEW QUESTION # 114
Network traffic coining from an organization's CEO must never be denied. Which access control policy configuration option should be used if the deployment engineer is not permitted to create a rule to allow all traffic?
- A. Configure a trust policy for the CEO.
- B. Create a NAT policy just for the CEO.
- C. Configure firewall bypass.
- D. Change the intrusion policy from security to balance.
Answer: A
NEW QUESTION # 115
On Cisco Firepower Management Center, which policy is used to collect health modules alerts from managed devices?
- A. correlation policy
- B. health policy
- C. health awareness policy
- D. access control policy
- E. system policy
Answer: B
Explanation: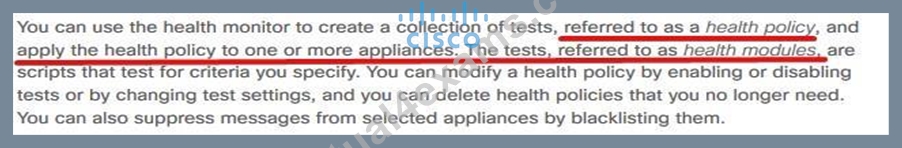
NEW QUESTION # 116
A network administrator is configuring Snort inspection policies and is seeing failed deployment messages in Cisco FMC.
What information should the administrator generate for Cisco TAC to help troubleshoot?
- A. A "show tech" for the Cisco FMC.
- B. A "show tech" file for the device in question.
- C. A "troubleshoot" file for the Cisco FMC.
- D. A "troubleshoot" file for the device in question.
Answer: C
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config- guide-v62/troubleshooting_the_system.html
NEW QUESTION # 117
How does Cisco Secure Cloud Analytics handle information about network traffic?
- A. It performs a heuristic analysis on events and network flow data.
- B. It performs a behavioral analysis on events and network flow data.
- C. It stores the information in a database without any analysis.
- D. It forwards the information to other devices without storing it.
Answer: B
Explanation:
Cisco Secure Cloud Analytics (formerly Stealthwatch Cloud) uses behavioral analysis to monitor events and network flow data. It builds a baseline of normal network behavior and then detects anomalies, such as data exfiltration or lateral movement, indicating potential threats.
NEW QUESTION # 118
Drag and drop the steps to restore an automatic device registration failure on the standby Cisco FMC from the left into the correct order on the right. Not all options are used.
Answer:
Explanation: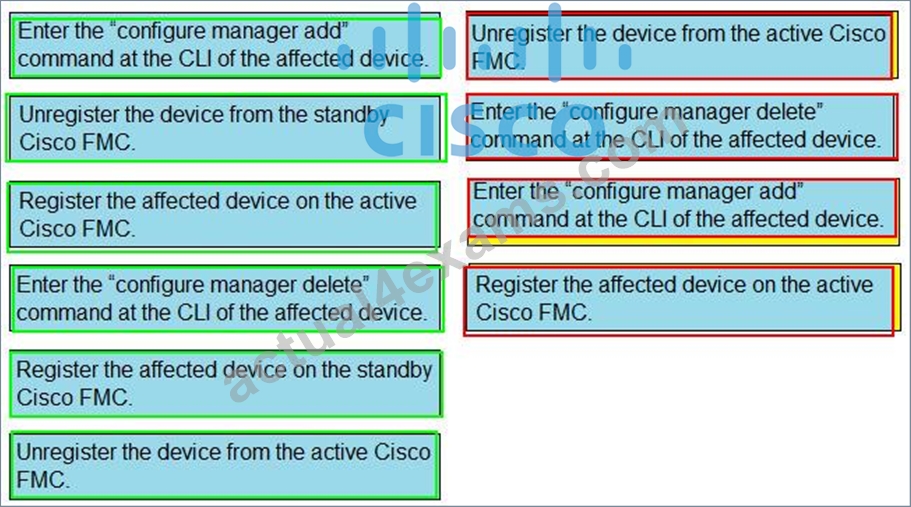
NEW QUESTION # 119
What is the maximum SHA level of filtering that Threat Intelligence Director supports?
- A. SHA-512
- B. SHA-4096
- C. SHA-256
- D. SHA-1024
Answer: C
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/623/configuration/guide/fpmc-config-guide-v623/cisco
NEW QUESTION # 120
An administrator is adding a QoS policy to a Cisco FTD deployment. When a new rule is added to the policy and QoS is applied on 'Interfaces in Destination Interface Objects", no interface objects are available What is the problem?
- A. QoS is available only on routed interfaces, and this device is in transparent mode.
- B. The network segments that the interfaces are on do not have contiguous IP space
- C. A conflict exists between the destination interface types that is preventing QoS from being added
- D. The FTD is out of available resources lor use. so QoS cannot be added
Answer: A
NEW QUESTION # 121
Which Cisco Advanced Malware Protection for Endpoints policy is used only for monitoring endpoint actively?
- A. audit
- B. Windows domain controller
- C. protection
- D. triage
Answer: A
Explanation:
Reference: https://www.cisco.com/c/en/us/support/docs/security/amp-endpoints/214933-amp-for-endpoints-deployment-methodology.html
NEW QUESTION # 122
......
Use Free 300-710 Exam Questions that Stimulates Actual EXAM : https://www.actual4exams.com/300-710-valid-dump.html
Get 100% Real 300-710 Free Online Practice Test: https://drive.google.com/open?id=1fa5wYERxsd52_69aEf_u9kt7kZpS_OCO